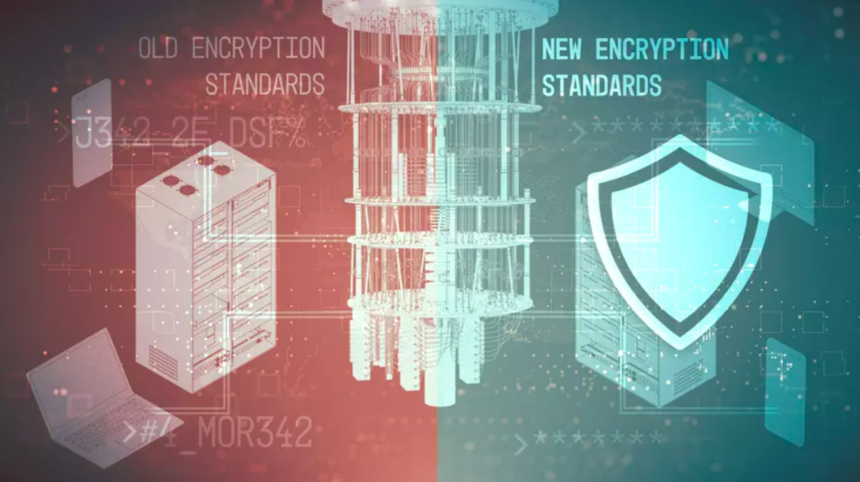
The National Institute of Standards and Technology (NIST) in the United States has released its high-level road map to help organizations switch to post-quantum cryptography (PQC) standards.
The NIST released the standards in August 2024. They were made to withstand the assault of a future quantum computer.
Through the report “Transition to Post-Quantum Cryptography Standards (NISTIR 8547), the agency outlines its official approach and timelines for transitioning away from quantum-vulnerable algorithms to quantum-resistant standards.
The report is the core technical document meant to inform federal agencies, industry partners and standards organizations about what needs to change and when during the migration to PQC standards — a cryptographic modernization with details that will vary by organization but timelines that apply broadly.
“The report describes different use cases and says why one migration might take longer than another,” said NIST mathematician Dustin Moody, who heads the PQC standardization project.
“We understand there’s not one strategy that fits all use cases, and we want to help people handle their migration while staying abreast of what’s changing,” said Moody.
While quantum computers are still in development, a sufficiently powerful device — known as a cryptanalytically relevant quantum computer — would threaten the encryption methods that protect our confidential electronic information, from email messages to financial statements.
Even though the transition to PQC is beginning before such a device appears, today’s encrypted data is already at risk from the “harvest now, decrypt later” threat, where adversaries collect sensitive data now with the intention of decrypting it when quantum technology matures.
This threat is one of the main reasons why the transition to PQC is urgent, driving the need to make changes on a well-considered schedule.
Also, National Security Memorandum 10 established the year 2035 as the primary target for completing the migration to PQC across federal systems.
Meanwhile, Executive Order 14412 accelerated this timeline, requiring federal high-value assets and high-impact systems to migrate by 2030 for key establishment and 2031 for digital signatures.
NISTIR 8547 supports these migration timelines. While the memorandum applies specifically to federal systems, many organizations that work with the federal government will be affected as well.
The NIST report identifies quantum-vulnerable algorithms among NIST’s existing cryptographic standards. The report then provides the transition plan for the quantum-vulnerable algorithms in these standards, referencing the post-quantum algorithm standards NIST published in 2024.
“We lay out how certain encryption algorithms people are using today will get phased out,” Moody said.
“It’s important to know how a given algorithm might be disallowed in federal systems after a certain date, for instance, or whether it will be allowed but at the user’s own risk. Factors like this can help an organization plan,” Moody added.
Because migration is a logistically complex undertaking, the report also helps delineate the numerous factors that organizations should consider to complete the process. Not only are an organization’s own system components important, but also its entire cryptographic supply chain.
Some actions may take priority over others, Moody said. For example, because of the “harvest now, decrypt later” threat, organizations might prioritize migrating to the PQC key establishment standard for data that is particularly sensitive or needs to be kept secure for a long time.
The report also discusses the option of taking a hybrid approach, in which an organization hedges its bets by combining conventional encryption with PQC, akin to using two padlocks on a door instead of one.
NIST accommodates this option, which has the advantage of being more conservative from a security standpoint but also demands more computational resources.
The publication’s contents complement the migration to PQC guidelines project at NIST’s National Cybersecurity Center of Excellence (NCCoE).
The project has established a cross-sector collaboration focused on the use of the NIST PQC standards — working on demonstrations of cryptographic visibility and risk management practices to prioritize migration to PQC.
Also, the project aims to highlight considerations of cryptographic agility and demonstrations of PQC implementations to support migration timelines.
“The new report can help you understand the standards and requirements of the migration while the NCCoE project can show you the practical tools and blueprints to get the job done,” Moody said.